 Schedule a Call
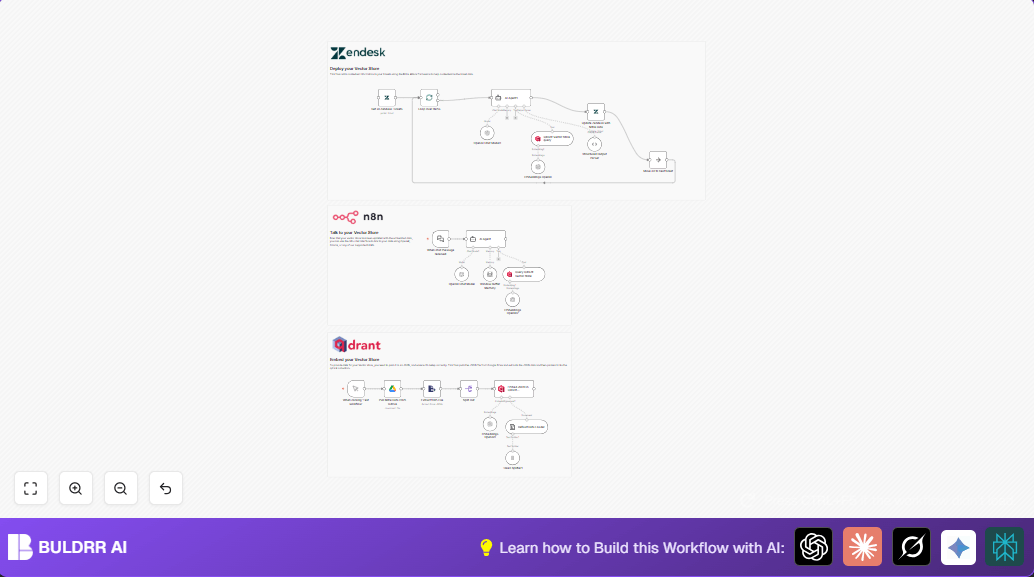
Automate Cybersecurity Incident Response with n8n & MITRE ATT&CK
This n8n workflow automates the analysis of SIEM alerts by extracting MITRE ATT&CK-based TTP data, generating actionable remediation steps, and updating Zendesk tickets. It helps security teams save hours on investigation and ticket enrichment by leveraging AI and vector stores.

 BULDRR AIAI ASSISTANT
Tap to talk
YOU